Showing posts with label System Center 2012. Show all posts

Monday, 22 February 2016

Automatically create Microsoft Office mobile apps for iOS and Android

System Center Configuration Manager landing page

This is another super-slick feature by the Microsoft ConfigMgr/Intune team. The announcement was made on the ConfigMgr Team Blog a couple of weeks ago. We were informed that a new Intune extension was available for ConfigMgr 2012 R2 SP1 (CU2 is required).


This is the new extension. What does it do for us?

Once enabled, the following Office apps for iOS and Android will be automatically created and available in the Configuration Manager console for deployment:
  • Microsoft Word
  • Microsoft Excel
  • Microsoft PowerPoint
  • Microsoft OneDrive
  • Microsoft OneNote
  • Microsoft Outlook
See the apps automatically created.

The deployment types are also automatically created. I carry out a lot of ConfigMgr/Intune deployments so this is a great time-saving feature for me.

This feature will now be included in the latest version of Configuration Manager (Current Branch). Intune extensions do not apply to Current Branch.
Until next time......

Monday, 11 January 2016

Installing Configuration Manager - Visual Studio Invalid license data. Reinstall is required.

This is an annoying little problem but very easy to solve. You are installing Configuration Manager (2012 or 1511) and you encounter this error.


Visual Studio 2010 Shell. Invalid license data. Reinstall is required.

Have a look at the slash.hta icon. It looks a bit funny.

This can happen if you accidentally choose Microsoft Visual Studio 2010 when you launch the wizard in the first instance (as I did).


No problem. Right click on splash.hta and choose "Open with". Now we can choose Microsoft HTML Application Host. However that doesn't work and you get the same error.

So how do we fix this? Don't worry - it's easy. We just have to change the association for the .hta file extension.


Open the Control Panel and launch Default Programs.


Find the .hta extension. See it's currently set to Visual Studio. Double-click the extension.


We're asked how we would like to open this file type. Choose HTML Application host.


Now we're back in business. See that the hta icon has changed.


Now launch splash.hta again....


...and continue with the installation.

I hope this saves you some time.

Monday, 4 January 2016

"We speak Geek" webinar - Feb 10th

I'm pleased to have been asked by Secunia (Flexera Software) to deliver a webinar as part of the "We speak Geek" series.

Intune is the Microsoft Mobile Device Management platform. It is the only MDM solution that can integrate with System Center Configuration Manager. Administrators can manage their on premise and mobile devices using a single console. In this webinar I will be discussing my favourite features of the solution.

The webinar is on February 10th at 4pm and is titled "5 really cool features of Configuration Manager with Intune". I hope you will be able to attend.

You can register here

https://www.brighttalk.com/webcast/8113/186135?source=gerryhampson

Until then.....

Friday, 11 December 2015

Patch third party applications

Back to Secunia menu

In the last blog post we deployed the CSI agent to our computer estate. Scans have been carried out and the information is now available in the Secunia CSI Portal.


See the top 10 "Most Prevalent Insecure Software Installations".

So how do we patch the insecure applications. Let's run through the process.


Navigate to Patching > Secunia Patching Systems. See the list of products that we can now patch. Choose the one you want. I'm going to patch VLC Media Player.


Right click and choose "Create Update Package".


The Package Configuration wizard is launched. Enter a suitable name.


Don't forget to select "Use Secunia Custom Naming".


Leave the defaults and click next to continue. Finally choose Publish.

(Note that the configuration options will vary depending on the application).


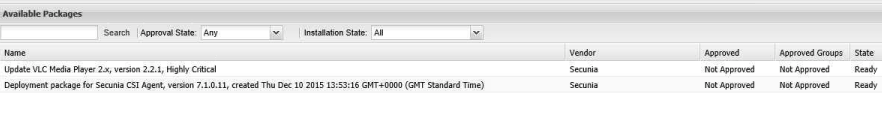
The package has been created and published to WSUS.


In ConfigMgr kick off a manual sync.


Accept that you want to site-wide sync.


The package is available in ConfigMgr almost immediately.


Right click the package and choose to deploy.


Run through the usual Deploy Software wizard.


Complete the wizard.


You have now completed the third party patch process. You can monitor the success of the deployment in Monitoring > Deployments.

I hope this series of blog posts has been useful for you.

Until next time.....

Inventory and CSI Agent

Back to Secunia menu

In order to have an effective third party patching solution you need to know what third party applications are on your computers. There are a number of ways to collect this inventory.

ConfigMgr Software Inventory
I'm not a real fan of software inventory in ConfigMgr. It doesn't gather the information from "Programs and Features" on your devices (ironically that is done by hardware inventory). Rather it just collects a lot of information about files on your systems. You have to configure the file extensions in advance. For me it causes a lot of unnecessary overhead for very little gain.

If you wish to use this method you must add the following file extensions to ConfigMgr software inventory.
*.exe
*.dll
*.ocx

Also the ConfigMgr server must have Internet access and be able to communicate with the Secunia cloud service using port 443.

Remote Scanning
This is OK for smaller networks but doesn't scale well to enterprises.


CSI Agent
This method requires that a small lightweight agent is installed on each computer. All computers will need Internet access and be able to communicate with the Secunia cloud service using port 443.This is the method we will use for this blog.

In the CSI Portal navigate to Patching > Agent Deployment.


Select "Create CSI Agent Package".


The Package Configuration wizard is launched. Enter a suitable name.


Make sure that you check the "Use Secunia Custom Naming" box. All third party updates will then have the Secunia name. You will be able to filter by Secunia and you will never exceed the vendor limit of your Software Update Point.


Choose the defaults. Remember that we will be publishing the package to WSUS.


The package has been created.....


.....and is available.

Now we must carry out some preparatory work in ConfigMgr. Open the Software Update Point properties.


Select "Create all WSUS reporting events".


Ensure "Security Updates" is selected.


For products note that we can currently only see Local Publisher and Microsoft.


Manually synchronize the updates.


Almost immediately you will see Secunia as an available option. Check the box.


In time the package will be available in ConfigMgr. This can take a while (almost an hour in this example).


Right click and choose to deploy the package.


Enter a suitable name for the deployment and choose the collection of devices.


This is a required deployment.


Choose as soon as possible.


A reboot is not required.


Select a deployment package.


Click Next to create the deployment.


Now you could wait until the normal updates cycles run. However I'm impatient so I've used the Now Micro Right click tools to immediately run the Software Updates Deployment Evaluation Cycle and the Machine Policy Retrieval and Evaluation Cycle. The agent now installs on the computers.


You can see scan results being reported in the CSI portal.


Detailed scan results.


See the insecure third party applications.


See the top 10 offenders. We will update these applications in the next blog in the series.

Until next time.....